Kai Werner · 28 September 2026
Examining Encryption Protocols and User Data Handling in Modern Note-Taking Platforms
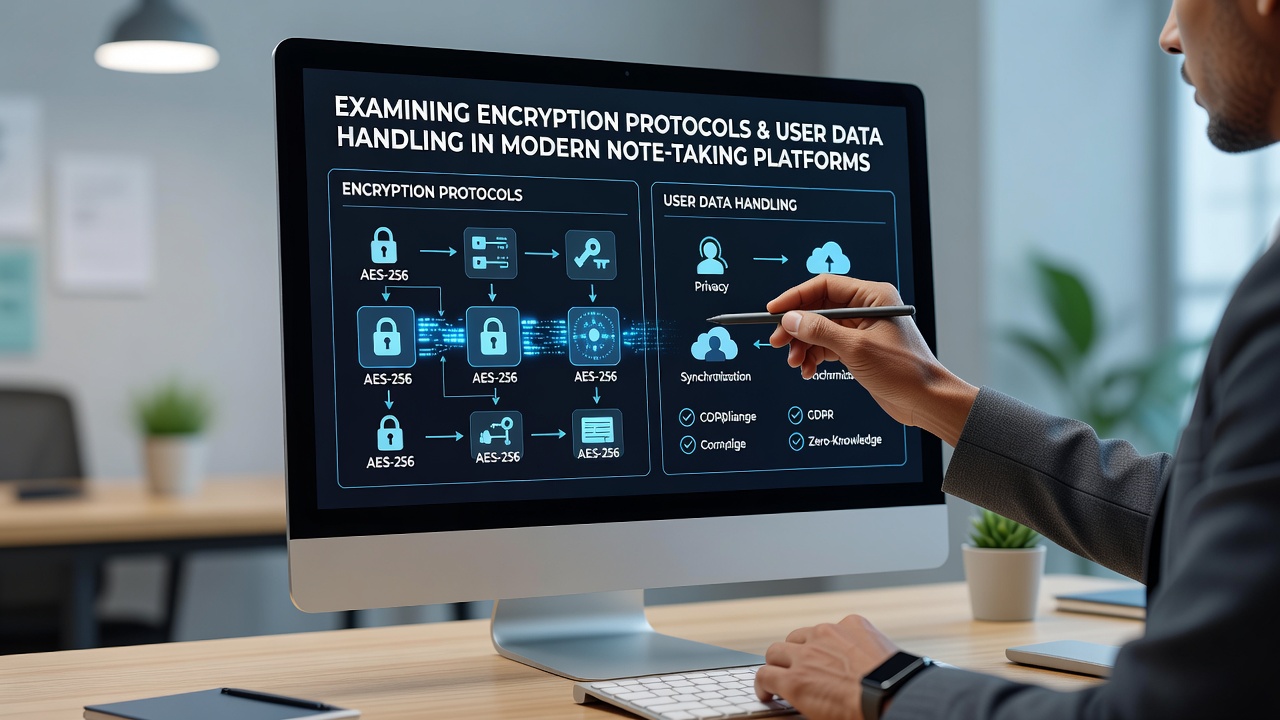
Researchers continue to track how note-taking platforms manage encryption and user information, with protocols evolving to address growing storage demands and regulatory requirements. Major services implement standards such as AES-256 for data at rest while combining transport layer security for data in transit, and these choices directly affect how notes remain protected across devices. Observers note that end-to-end encryption appears in select applications where users control the keys, whereas server-side encryption remains common in others that prioritize recovery features and multi-device synchronization.Core Encryption Standards in Use
Platforms rely on established cryptographic methods to safeguard stored content, and data shows AES-256 serves as the baseline for most providers because it balances performance with resistance to known attacks. Some applications layer additional controls such as zero-knowledge architectures, which prevent the service provider from accessing decrypted notes even under subpoena requests. Experts point out that key management varies widely, with certain tools generating keys locally on user devices while others store them in secure enclaves managed by the company. In September 2026 several services plan to roll out updated key rotation schedules in response to new hardware security module guidelines from standards bodies.
Transport security follows TLS 1.3 in the majority of current deployments, and this reduces exposure during synchronization between mobile and desktop clients. Those who examine audit reports find that independent verifications confirm implementation details yet also highlight occasional gaps in older legacy code paths. Researchers discovered through penetration testing that weak random number generation in early versions created predictable patterns in some note identifiers, prompting widespread patches across the sector.
User Data Handling Practices
Handling of user information extends beyond encryption to include access logging, retention periods, and deletion workflows. Companies maintain detailed records of login attempts and content changes to support troubleshooting, yet these logs themselves require protection under the same encryption layers applied to notes. Data handling policies often specify retention windows measured in months rather than years, with automatic purging triggered after account inactivity thresholds are reached. Observers note that export functions allow users to retrieve content in standard formats, and this capability helps maintain portability when switching providers.
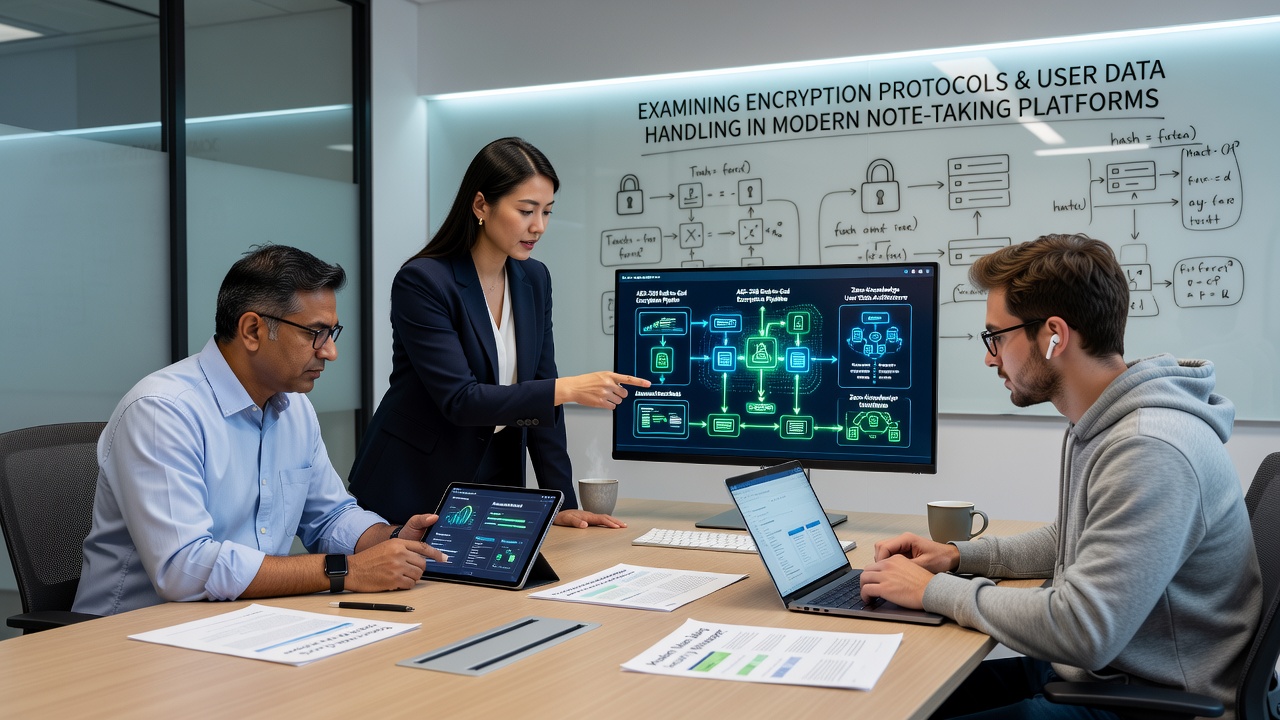
Metadata attached to notes receives separate treatment in many systems, with timestamps and folder structures sometimes stored in plaintext indexes to enable fast search. This separation creates trade-offs because attackers who gain partial access might still reconstruct activity timelines even without reading note contents. Services address this through tokenization techniques that replace identifiable elements with random identifiers before indexing occurs. Figures from industry reports indicate that average daily note creation volumes exceed several million entries across leading platforms, underscoring the scale at which these protections must operate reliably.
Regulatory Compliance and Geographic Variations
Compliance frameworks shape data handling choices, and providers serving international users adapt storage locations and access controls to meet regional mandates. The European approach emphasizes data minimization and user consent mechanisms, while Canadian standards focus on accountability through documented breach notification timelines. Australian privacy requirements add emphasis on cross-border transfer restrictions that affect how multinational platforms replicate data across regions. One study revealed that organizations aligning encryption key storage with local jurisdiction rules experienced fewer regulatory inquiries during audits.
Breaches remain a documented risk, and public disclosures show that compromised employee credentials rather than flaws in encryption algorithms caused most incidents involving note platforms. Response protocols now include mandatory customer notifications within fixed windows, and this transparency has driven adoption of additional monitoring tools such as anomaly detection on access patterns. Those who've studied breach reports find that rapid key revocation capabilities limit the window during which stolen credentials remain useful.
Emerging Developments
Quantum-resistant algorithms receive increasing attention as computational capabilities advance, adn several platforms have begun testing hybrid schemes that combine classical and post-quantum methods for long-term note archives. Integration with hardware security features in modern devices allows local encryption operations to occur without exposing keys to the operating system. Data indicates that adoption rates for these enhanced features vary by user segment, with enterprise customers requesting them more frequently than individual subscribers.
Conclusion
Encryption protocols and data handling procedures in note-taking platforms continue to adapt to technical threats and regulatory landscapes. Organizations document their approaches through public security whitepapers and third-party audits, giving users concrete information when selecting services. Continued monitoring of implementation details remains essential as new standards emerge and usage patterns shift across different regions.